

⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯A closed-source, web-driven deployment appliance running on Windows: automated Windows installs + multi-distro Linux live boot over LAN / VLAN / Layer-2 VPN / WiFi. Coexists with existing pfSense / OPNsense / router DHCP, or runs isolated for air-gapped labs. Dashboard: | Boot plane: :6824 | Internet once, then fully offline.
TABLE OF CONTENTS
- What is SEZOY? Why should homelab care?
- Where does SEZOY fit in your homelab?
- Infra wins: coexistence, smart boot, WiFi boot
- Bulk Windows rollout with pristine ISOs
- Multi-distro Linux netboot + hardware diagnostics
- Ops: live view, backup, automation API
- Requirements and networking
- TEST SEZOY from the Internet WITHOUT installing SEZOY (VMware / Proxmox-bridged VM + SoftEther VPN)
- Run your own SEZOY in your lab
- Lab FAQ
- Notes for shared stress-testing
⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯⎯
1. What is SEZOY? Why should homelab care?
SEZOY is closed-source software (prebuilt installer, no code to review) that turns one Windows machine into a full network deployment server. You manage everything in a modern web dashboard (English / Vietnamese / Chinese / Japanese, multiple themes, tray icon). Clients - bare metal, VMware, Proxmox, Hyper-V, VirtualBox - just network-boot into a menu, pick a Windows/Linux ISO and go.
For ServeTheHome folks, the pitch is: low-touch, coexistence-friendly, easy to scale:
- No USB, no re-flashing: new Windows build or Linux distro = swapping one ISO file on the server.
- Coexists with your stack: already running pfSense / OPNsense / router DHCP? SEZOY runs in "boot-info only" mode and never fights for IPs. Isolated rack / VLAN? SEZOY serves addresses itself.
- One ISO serves the fleet: the same Windows ISO can carry different configs for different node groups (vendor, model, MAC, RAM/disk, UEFI/Legacy, SecureBoot state, NIC type…). Each node auto-gets the right one.
- Remote boots like local: join over Layer-2 VPN and a far node boots as if on the same switch - handy for distributed labs.
- Offline-first: from the second run it deploys with no Internet - air-gapped labs, exam rooms, isolated racks.
- See the fleet: per-node screens in the browser (Full HD), progress %, per-node logs, remote shutdown / reboot / continue.
2. Where does SEZOY fit in your homelab?
Three common fits:
- Same LAN as your existing router (recommended): SEZOY + router share the subnet. SEZOY only adds boot info; the router still owns IPs. No re-architecture, no outage risk.
- Isolated lab / VLAN / back-to-back cable / test VPN: SEZOY hands out client IPs itself (default .200–.250, pool/gateway/DNS editable). Good for test racks, private Proxmox clusters, exam nets.
- Wireless boot: the server becomes a hotspot for HTTP-Boot-capable nodes. No capable card? Soft warning only; wired boot keeps working.
Either way: correct-NIC binding, separate WiFi address, no leaked broken addresses - lessons learned from long-distance VPN testing.
3. Infra wins: coexistence, smart boot, WiFi boot
- Two clear DHCP modes: share-the-network (no IP fights) or self-serve (private nets). Editable right in the UI: server IP, netmask, gateway, DNS, pool.
- Step-aware boot: the server knows which stage each node is at (just powered on / mid-load / ready for high-speed fetch) and hands the right boot file per stage. Small seed files first, then straight to high-speed HTTP, and over long-distance VPN.
- Broad support: Legacy PXE, UEFI PXE, iPXE, wired + wireless HTTP Boot. SecureBoot-ON boots fine (signed Windows boot files, per-family Linux signing). Slim builds for old boxes.
- Loop guard: a node rejected and retrying in a loop gets a help screen instead of hammering forever - fewer 2am lab rescues.
4. Bulk Windows rollout with pristine ISOs
One rule: ISOs on the server stay pristine. Everything else arrives at boot time over HTTP.
For operators that means:
- Reusable templates: each holds computer name (random or LAB-A-* rules), key (empty = existing digital license), language/keyboard/timezone, domain join, accounts + auto-logon, slim OOBE (skips forced online account/WiFi/BitLocker on 24H2+), 2-layer privacy, 4-stage scripts, apps to install, junk to remove, drivers/updates to load. Preview + pre-flight checks, 1-click duplicate.
- Two styles: fully automatic for bulk; stock Setup screens for odd machines/quick tests (with Win11 check skips when wanted).
- Dynamic drivers: shared driver/patch/app catalog for every template. Fix once, every node benefits. Adding a driver = one catalog entry, no image rework. Skipped entirely (saving 5–10s/node) when a template needs nothing.
- Safer accounts: temporary elevated account guarantees setup, then auto-demotes to standard user if selected.
- 100 nodes, different names/apps? Configure once, boot and done. Per-app success/fail reports come back to the dashboard.
5. Multi-distro Linux netboot + hardware diagnosticsClosed-source installer, online activate once then offline use. No usage-data collection, no activation-crack tools. Bring your own genuine ISOs + valid licenses.
- Many distros: Ubuntu / Mint, Debian, Kali, Arch, CentOS / Rocky / Alma / Fedora, antiX, Deepin… Auto-detected in-ISO, boot entries auto-built, missing firmware fetched.
- True live boot: kernel + system load directly over the network, merged with add-on packs (drivers, firmware, WiFi, diagnostics) into one working system - WiFi works, installable - original ISO untouched.
- Ventoy fans: Ventoy/iVentoy-style add-on packs for Win + Linux, built once per distro, faster on later boots.
- Built-in live hardware-check ISO: graphical node info, deep CPU/RAM/disk/memory tests, temps, risk score, report export. Fits the "receive old node => check => install Windows" homelab flow.
6. Ops: live view, backup, automation API
- Overview: node totals, running jobs, health, CPU/RAM/disk bars.
- Live view: auto-refreshing online-node grid, click for large/fullscreen, shutdown/reboot/remote/continue/custom commands, blinking control state. Filter by status (booting/installing/done/error/waiting), search by MAC/hostname, per-node history.
- Logs & reports: filter by node/event/date, export; CSV/HTML/PDF reports.
- Serious backup: encrypted on-box storage, 1-click backup, daily/weekly/monthly auto schedule + retention + last/next display. Restore with overwrite warning.
- Command API + bundled docs: create/edit/delete templates and groups, bulk CSV import, online nodes + screenshots, remote deploy, logs/stats, access-code management (shown-once, masked/enable/revoke/renew, expiry, granular permissions). Enough for lab portals, per-class templates, bot/dashboard integrations. Two-layer security: web session + per-node boot code.
- Self-served tool pack: genuine Microsoft ISO fetcher + Server 2016/2022/2025 (multi-thread, resume), ISO open/split, offline Windows app store, driver packs with %/speed/ETA, self-update.
7. Requirements and networking
- Server: Windows 10/11 x64 or Server 2022/2025, Admin, ≥8GB RAM (16GB+ for many nodes), disk for ISOs (Windows 5–7GB each, Linux 2–4GB each). Hotspot-capable WiFi card only for wireless boot.
- Nodes: bare metal or VM (VMware / Proxmox / ESXi / Hyper-V / VirtualBox) with PXE or HTTP Boot, ≥4GB RAM for the install env.
- Network: same L2 (LAN/VLAN/bridged VPN). Internet once for first-run tools; fully offline after.
- Ports: 5893 dashboard (HTTPS), 6824 boot (HTTP), 67/68 addressing, 69 seed files, 10809 network disk (if used). Allow the "SEZOY Service" firewall entry.
8. TEST SEZOY from the Internet WITHOUT installing SEZOY (VMware / Proxmox-bridged VM + SoftEther VPN)
8.1. Step 1 - SoftEther VPN Client + virtual NICThe owner runs SEZOY on machine B (192.168.251.1) with a public test VPN Hub. You (machine C) join the same L2 over VPN and bridge your test VM straight into the VPN NIC - it PXE-boots from the remote server as if on the same switch. Shared dashboard: (if given access).
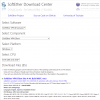
- Install SoftEther VPN Client (tick SoftEther VPN Client).
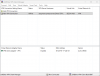
- Client Manager => New Virtual Network Adapter => memorable name (SEZOY-VPN) => Enable.
- New VPN Connection Setting:
- Host Name: sezoyhost.vpnazure.net
- Port: 443
- Virtual Hub Name: SEZOY.HUB
- User Name: tester99
- Password: tester99
- Must check the "No Adjustments of Routing Table" checkbox in the window of "Advanced Settings..." button, or import the VPN config file in the attachment
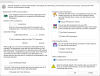
- Rest default.
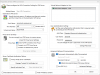
- Double-click => Connected. Errors 1/2/691 => recheck hub/user/pass, port 443 firewall.
8.2. Step 2 - HARD-bridge the VM to the VPN NIC (mandatory)
Never leave bridging on Automatic - the VM will grab the wrong IP from your home router.
- VMware Workstation Pro: Edit => Virtual Network Editor (Admin) => free VMnet (e.g. VMnet0, Bridged) => Bridged to = exactly the SoftEther virtual NIC => VM uses Custom: VMnet0.
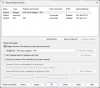
- Proxmox / Linux equivalent: attach the test VM NIC to the bridge holding the VPN client interface (vmbr bound to vpn_* / tap_*), disable test firewalls if needed, ensure DHCP broadcasts from 192.168.251.1 reach the VM.
- Suggested VM: UEFI firmware (try Legacy after UEFI passes), ≥4GB RAM, ≥40GB disk, e1000 first (then vmxnet3/virtio), Network Boot / PXE first.
8.3. Step 3 - Boot and record
- Power on => PXE => DHCP from 192.168.251.1 => SEZOY menu (allow 5–15s over Internet).
- Pick the shared ISO + tester template => deploy.
- Record: distro/edition, UEFI/Legacy, NIC model, SecureBoot ON/OFF, boot time, errors + MAC + screenshots.
- Done: clean VM shutdown => Disconnect VPN to free the IP.
8.4. Common lab issues
| Symptom | Fix |
|---|---|
| No DHCP / straight to BIOS | Wrong bridge (Automatic) - re-pin |
| DHCP OK but seed-file timeout | Low VPN MTU / firewall - retry, firewall-off test |
| Menu up but slow fetch | Normal WAN jitter, don't reboot in loops (loop-guard) |
| SecureBoot rejects loader | Screenshot, try SecureBoot OFF to isolate |
| VM gets home IP instead of 192.168.251.x | Bridge still wrong - recheck VMnet/bridge |
- Open .
- Serving NIC: the LAN/VPN/VLAN NIC to serve (not WAN NAT). Check the "SEZOY Service" firewall rule.
- Add ISOs: copy into the ISO folder or fetch directly (genuine Microsoft + Server 2016/2022/2025); click an ISO for live editions; pick an edition => fully automatic, leave empty => stock Setup; multi-mode for multi-group.
- Templates + groups: build presets, attach driver/app catalog, OOBE/scripts/cleanup/domain; group rules by vendor/model/MAC/RAM/disk/boot/SecureBoot/NIC (simulator first); pool/gateway/DNS, WiFi name if needed.
- Start Boot Server => share-the-network (DHCP present) or self-serve (isolated) => WiFi AP if wanted => PXE-boot nodes => pick ISO => auto-assigned template => auto install => watch screenshots/progress/reports. Enable auto backup.
10. Lab FAQ
- Disable lab SecureBoot? No - signed paths for both Windows and Linux.
- Already have DHCP (router/pfSense)? Use share-the-network mode, no fights.
- Fully air-gapped? Yes - Internet once, offline 100% after.
- Automation? Bundled API docs + access codes integrate portals/bots/dashboards.
- Lost config? Restore from backup (auto schedule).
- Wireless boot needs? Hotspot-capable server card + HTTP-Boot-capable node. Wired works regardless.
11. Notes for shared stress-testingTested via the VPN above? Reply with: hypervisor + VM config (UEFI/Legacy, NIC model, RAM), distro/edition booted, SecureBoot ON/OFF, boot time, menu screenshot - so SEZOY can improve. Thanks STH folks!
This test box is modest, on WiFi over the Internet - not a fiber rack. Read this so everyone's turn goes smoothly.
- NEVER stop the Boot Server / quit the host app (if given dashboard access). If stopped: dashboard => Start Boot Server => VPN card (192.168.251.1) => self-serve IP mode. Report sudden menu loss with the time.
- Test pool is only ~50 IPs (.200–.250). Hard-killed/frozen/dropped VMs hold slots. Golden rule: clean shutdown => Disconnect VPN.
- One VM per person. Light boot first (Linux live, hardware-check ISO), then full Windows (gigabytes over VPN, slowness is normal).
- Node sessions expire after 5 idle minutes - re-boot fresh instead of clicking around.
- Report properly: hypervisor + VM config, NIC, SecureBoot, screenshot + MAC, test time (VN time).
- Maintenance windows: skim the topic for downtime notices before testing.
12. Download
- Home page: https://tekdt.xyz/en/download
- Github Release: GitHub - tekdt/sezoybin
Attachments
-
 33.1 KB Views: 32
-
 69.4 KB Views: 32
-
812 bytes Views: 0
Last edited:

